Beyond yes or no
Ask what a user can do, and who can do it
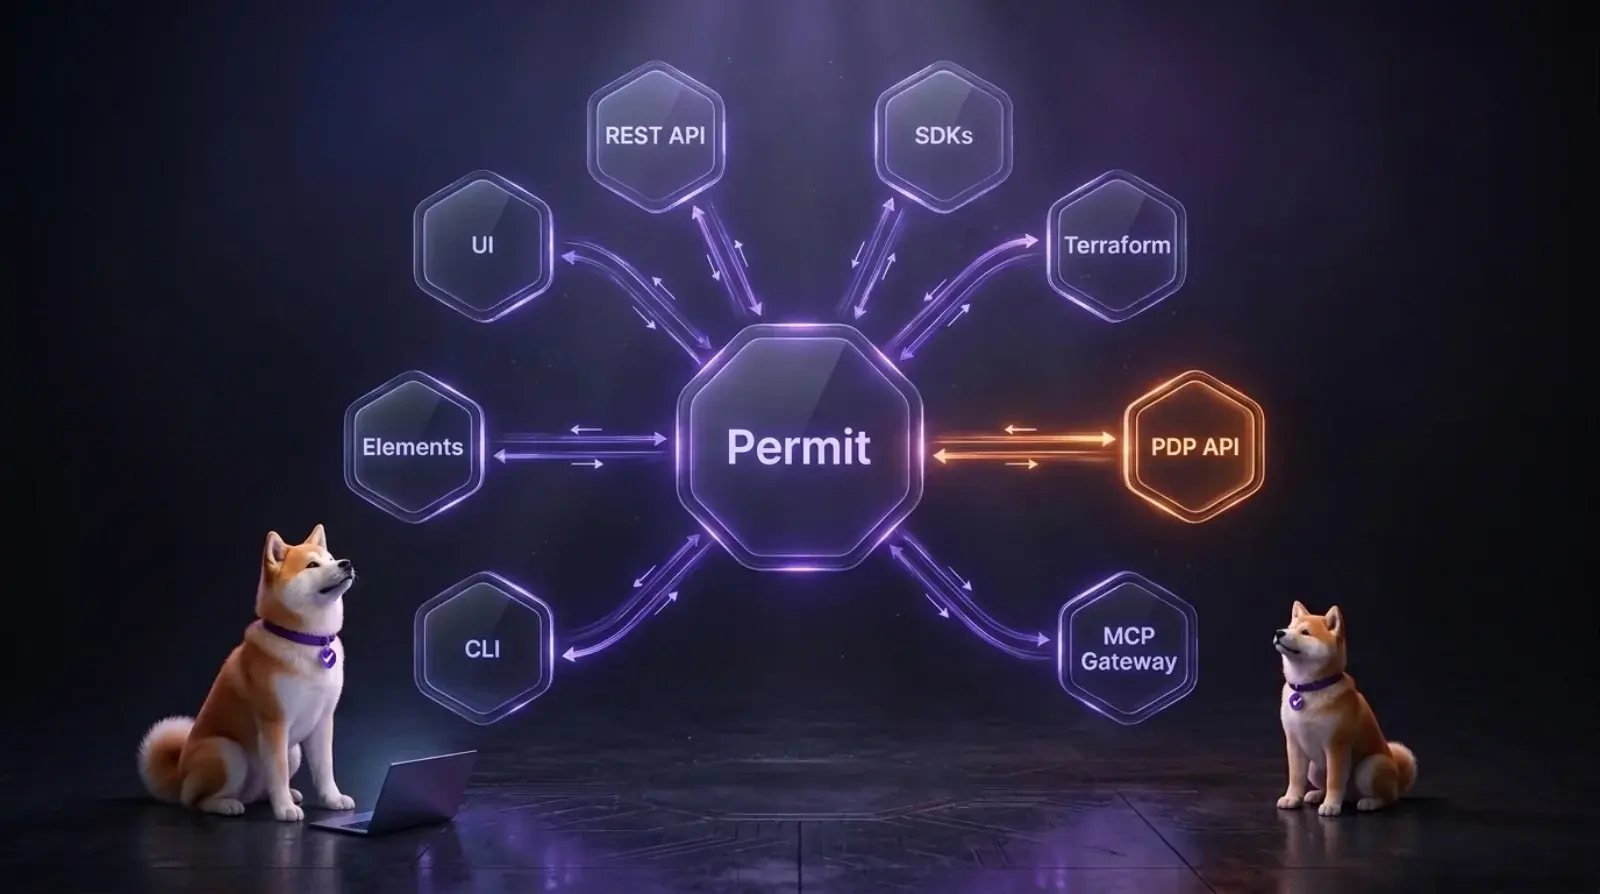
A single check answers one question. Real products need lists: which actions to show this user, which users to offer in a share dialog, and who should get this approval request. Permit answers both directions from the same policy, so the UI never disagrees with enforcement.
- get_user_permissions returns everything a user can do, across tenants and resources, filterable by tenant, resource, or resource type.
- authorized_users returns every user who can take an action on a resource type or a specific instance, with the role assignments that granted it.
- bulk_check evaluates many checks in one request, for lists and dashboards.
- Attribute conditions can be included in both queries when you opt in, since they cost more to compute.
invoice_access.py
import os
from permit import Permit

permit = Permit(
    token=os.environ["PERMIT_API_KEY"],
    pdp="http://localhost:7766",
)

# What can dana do? Show only actions that will succeed.
perms = await permit.get_user_permissions(
    "dana@example.com", tenants=["example-co"]
)

# Who can approve invoice 8841? Route the request there.
approvers = await permit.authorized_users(
    "approve", "invoice:8841"
)